
What Is DKIM2? The Email Authentication Upgrade Coming in 2026
Email authentication has barely changed in a decade. SPF, DKIM, and DMARC are still the "big three," and they still break in all the same ways: a mailing list adds a footer, a security gateway rewrites a link, a forwarding rule strips a header — and a perfectly legitimate message lands in spam.
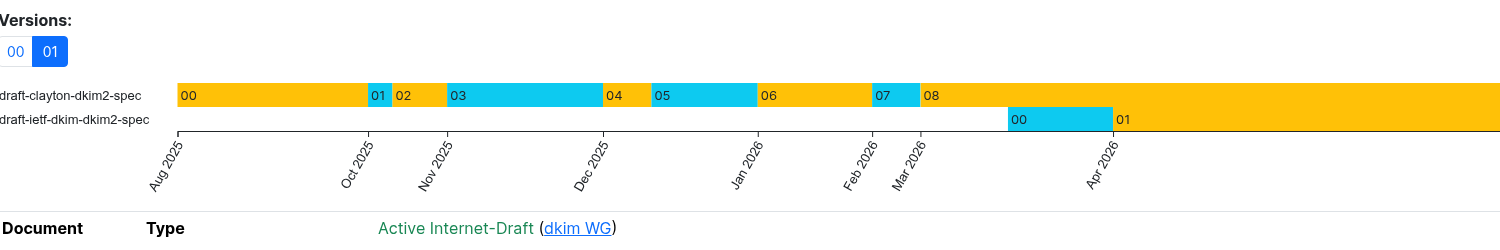
That's about to change. On March 18, 2026, the IETF DKIM Working Group formally adopted a successor specification: DKIM2. The first official working-group draft, draft-ietf-dkim-dkim2-spec-01, was published on April 20. And according to deliverability researchers tracking the proposal, the first mailbox providers will start signing with DKIM2 within months — with major providers expected to follow before the end of 2026.
Here's what's actually different, and what you need to know before it lands.
The Problem DKIM2 Is Solving
DKIM works by signing a hash of the message body and selected headers with a private key. The receiver fetches the public key from DNS, recomputes the hashes, and verifies. If the message hasn't changed in transit, the signature passes. If a single byte of the body has changed — even a trailing newline — it fails.
That's a problem because the modern mail system constantly changes messages in transit:
- Mailing lists prepend
[list-name]to the subject and append unsubscribe footers. - Security appliances rewrite URLs through their own click-tracking domains.
- Forwarding rules strip or rewrite headers.
- Antivirus gateways mutate MIME structure to neutralize attachments.
Every one of these breaks DKIM. And when a sender publishes p=reject in their DMARC policy — as Yahoo and Google now effectively require for bulk senders — broken DKIM means the message is rejected outright, not just sent to spam.
Why ARC Didn't Fix It
ARC (Authenticated Received Chain) was the previous attempt to solve this. The idea: each forwarder adds an ARC seal stating "when I received this, the authentication was valid." Receivers could then trust the chain of seals back to the original sender.
It didn't work in practice. As Laura Atkins of Word to the Wise recently summarized, "most receivers tell us they can't use or trust ARC signatures." The problem is that ARC asks you to trust the intermediary's claim about what happened, without giving you any way to verify it. Worse, an ARC seal doesn't tell you what the intermediary changed — only that they vouched for it. The IETF DMARC working group is now actively working on a draft to deprecate ARC.
How DKIM2 Actually Works
DKIM2 takes a fundamentally different approach: document the modifications, don't just trust the modifier.
The originator signs the message with a DKIM2-Signature header that includes i=1. When a forwarder modifies the message, instead of just resealing the new version, it records exactly what changed (the added footer, the rewritten URL, the new subject prefix) and adds a new signature with i=2. The next forwarder adds i=3, and so on.
The result is a fully linked chain of custody from sender to recipient. The receiving server checks the highest-numbered signature first, then walks the chain backwards. Because each modification is documented, the receiver can undo the changes step by step and verify the original signature on the unchanged message — exactly as the sender wrote it.
Three things follow from this design that ARC couldn't deliver:
- Forwarding stops breaking authentication. Mailing lists, forwarding rules, and security gateways can modify messages freely as long as they document what they did. The original signature still validates.
- Replay attacks get harder. Each signature is bound to the recipient address of the previous hop. A signature stolen from one delivery can't be replayed to a different address — the chain won't link.
- Backscatter goes away. Bounces and delivery status notifications must travel back along the same signed chain. A bounce can only go to a domain that actually sent the message, and can only come from a domain that received it. Forged bounces — the bane of every postmaster — stop working.
What You Need to Do (Spoiler: Almost Nothing, Yet)
DKIM2 is still a draft. The current revision, -01, expires October 22, 2026, and full RFC publication is years away. There are no DKIM2 toggles in Gmail, Outlook, or any major ESP yet. Don't change anything in production today.
What you should do this quarter:
- Get DKIM1 right. If you're still relying on shared signing domains from your ESP, move to a custom signing domain that aligns with your
Fromaddress. Senders who haven't sorted DKIM1 alignment by the time DKIM2 ships will be in worse shape, not better. - Tighten your DMARC policy. If you're still on
p=noneorp=quarantine, plan a path top=reject. DKIM2 makesp=rejectsafer to maintain because forwarding stops breaking your messages. - Plan to publish DKIM2 keys alongside DKIM1. The two protocols are designed to coexist. Early adopters will sign with both. Make sure your DNS provider supports the additional TXT records you'll need.
- Watch your ESP. If you send through a major provider, ask them when they plan to support DKIM2 signing. The big players are tracking the spec — Yahoo, Google, and Fastmail all have engineers on the author list (Richard Clayton, Wei Chuang, and Bron Gondwana respectively).
The Bigger Picture
DKIM2 is the first significant change to email authentication infrastructure since DMARC was published in 2015. The fact that engineers from Yahoo, Google, and Fastmail co-authored it together — and that the working group reached consensus on adoption within seven months of the first draft — signals that the major mailbox providers see this as overdue. ARC's failure to deliver on the forwarding promise has been a quiet pain point for everyone running modern mail infrastructure.
If the timeline holds and major providers ship DKIM2 support before the end of 2026, the practical effect for HTML email developers will be subtle but real: the long tail of "weird deliverability bugs" caused by intermediate forwarders will start to shrink. Mailing lists will work again. Auto-forwarders will stop trashing your password resets. The cases where you ship a perfectly authenticated message and it still ends up in spam because someone in the delivery path touched a header — those will start going away.
Bottom Line
DKIM2 isn't shipping in your account dashboard tomorrow. But the foundation just got laid this month, and it's the most consequential authentication change in a decade. If you've been ignoring the slow build-up around DKIM2, this is the moment to start paying attention.
For developers actively shipping HTML email, the immediate priority is the same as it's always been: get the basics right. Use a custom signing domain. Align From, SPF, and DKIM. Move toward p=reject. Test your templates rigorously across clients (we built Postdrop for exactly that). And if you want a refresher on how authentication works today before DKIM2 lands, our SPF, DKIM, and DMARC explainer covers the current model end-to-end.
Further reading: the official IETF draft, Laura Atkins' DKIM2 explainer at Word to the Wise, and the All About Email newsletter's DKIM2 update with a useful timeline of provider rollout expectations.